What this board proves
APNs certificate issuance, configured macOS compliance controls, configured FileVault controls, and the availability of Platform SSO settings in Intune.
Project 5 · sanitized evidence
This evidence page publishes a sanitized derivative of screenshots captured during the real Intune work. It proves specific Microsoft-side configuration and capability without implying ABM, ADE, or managed-Mac validation.
Screenshot proof board
The source captures show Apple Push certificate issuance, the macOS compliance baseline, the FileVault Settings Catalog profile, and Platform SSO capability in the real Intune tenant.
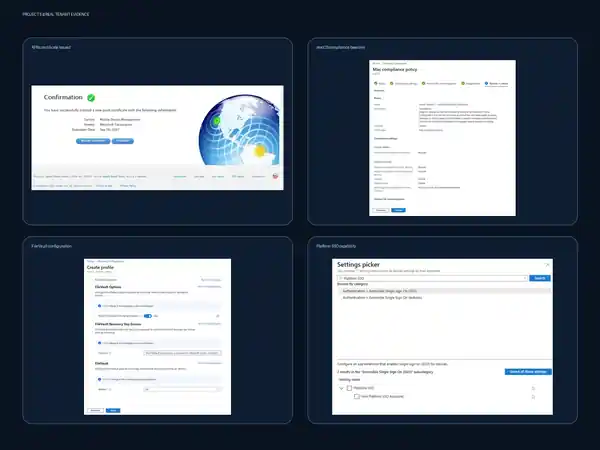
APNs certificate issuance, configured macOS compliance controls, configured FileVault controls, and the availability of Platform SSO settings in Intune.
Apple Business Manager enrollment, ADE execution, FileVault recovery-key escrow, Platform SSO endpoint registration, EAP-TLS authentication, application installation, or lifecycle actions on a managed Mac.