01 / Identity & access
Windows LAPS & Advanced Group Policy
Sanitized retrieval output records an EncryptedPassword source and successful authorized decryption.
Inspect the authorized retrieval result →Jeremy Fontenot / Abbeville, Louisiana
Windows Server · Active Directory · Microsoft Entra · Infrastructure Operations
Enterprise IT support experience paired with hands-on Windows Server, Active Directory, Microsoft Entra ID, Microsoft 365, virtualization, and PowerShell administration. Explore 15 documented projects and their supporting technical evidence.
The background behind the work
SUPPORT / INVESTIGATE / DOCUMENT / VALIDATE
Selected work
01 / Identity & access
Sanitized retrieval output records an EncryptedPassword source and successful authorized decryption.
Inspect the authorized retrieval result →11 / Endpoint management
Post-Autopilot output records Entra join, successful device authentication, and an Azure AD primary refresh token.
Inspect the device and SSO output →08 / Troubleshooting
The retained Linux01 record documents an SSSD responder conflict, the correction, and successful AD identity lookup and SSH afterward.
Read the remediation record →13 / PowerShell & Graph
Seven retained reporting scripts plus a new read-only Graph JSON export application, validated with eight passing Pester tests. Original code and test files are publicly inspectable; tenant data stays private.
Inspect the directory-role reporting code →05 / Virtualization
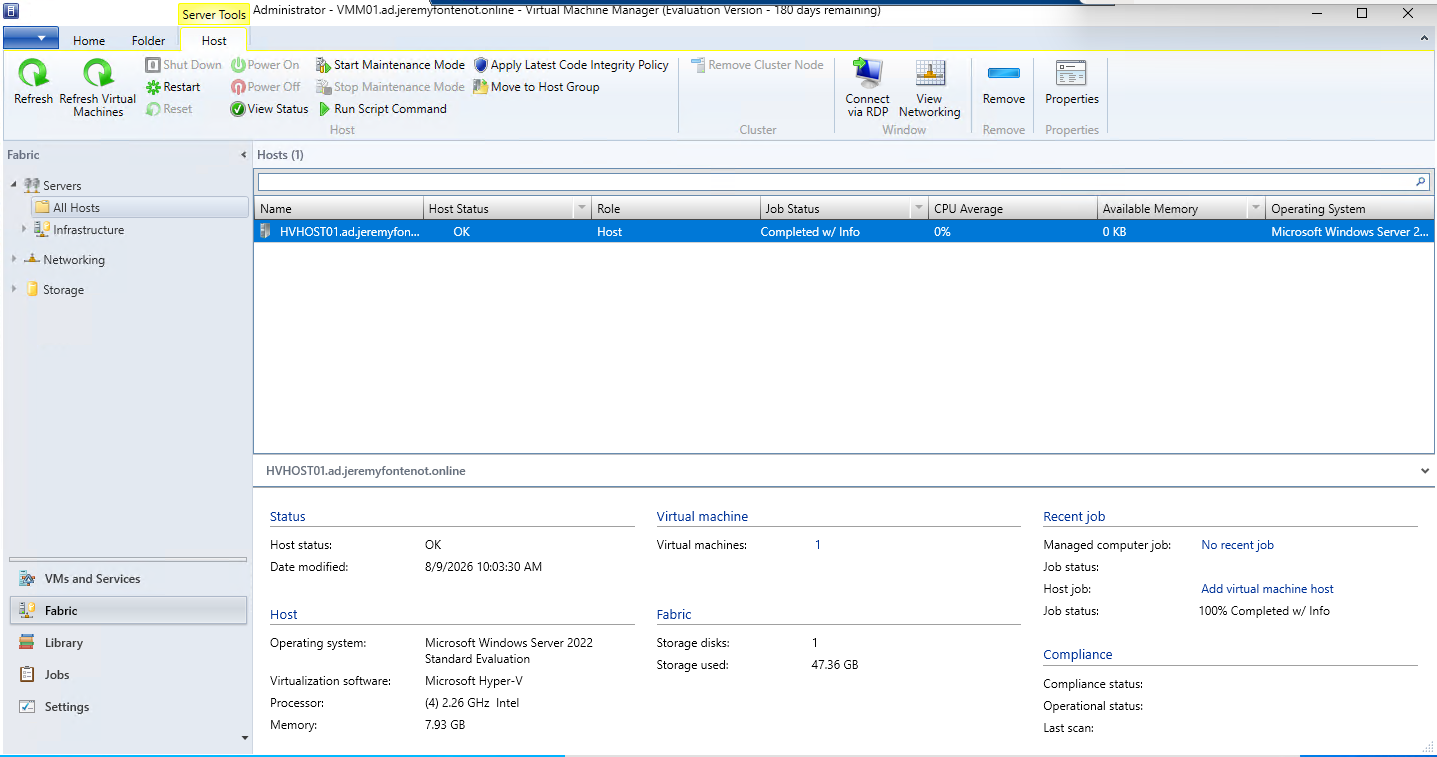
Managed-host console capture records HVHOST01 with host status OK and one virtual machine.
Inspect supporting artifact →10 / Microsoft 365
Sanitized Exchange output records shared-mailbox permissions and delegation; licensing discrepancies remain documented.
Inspect supporting artifact →14 / Identity & SSO
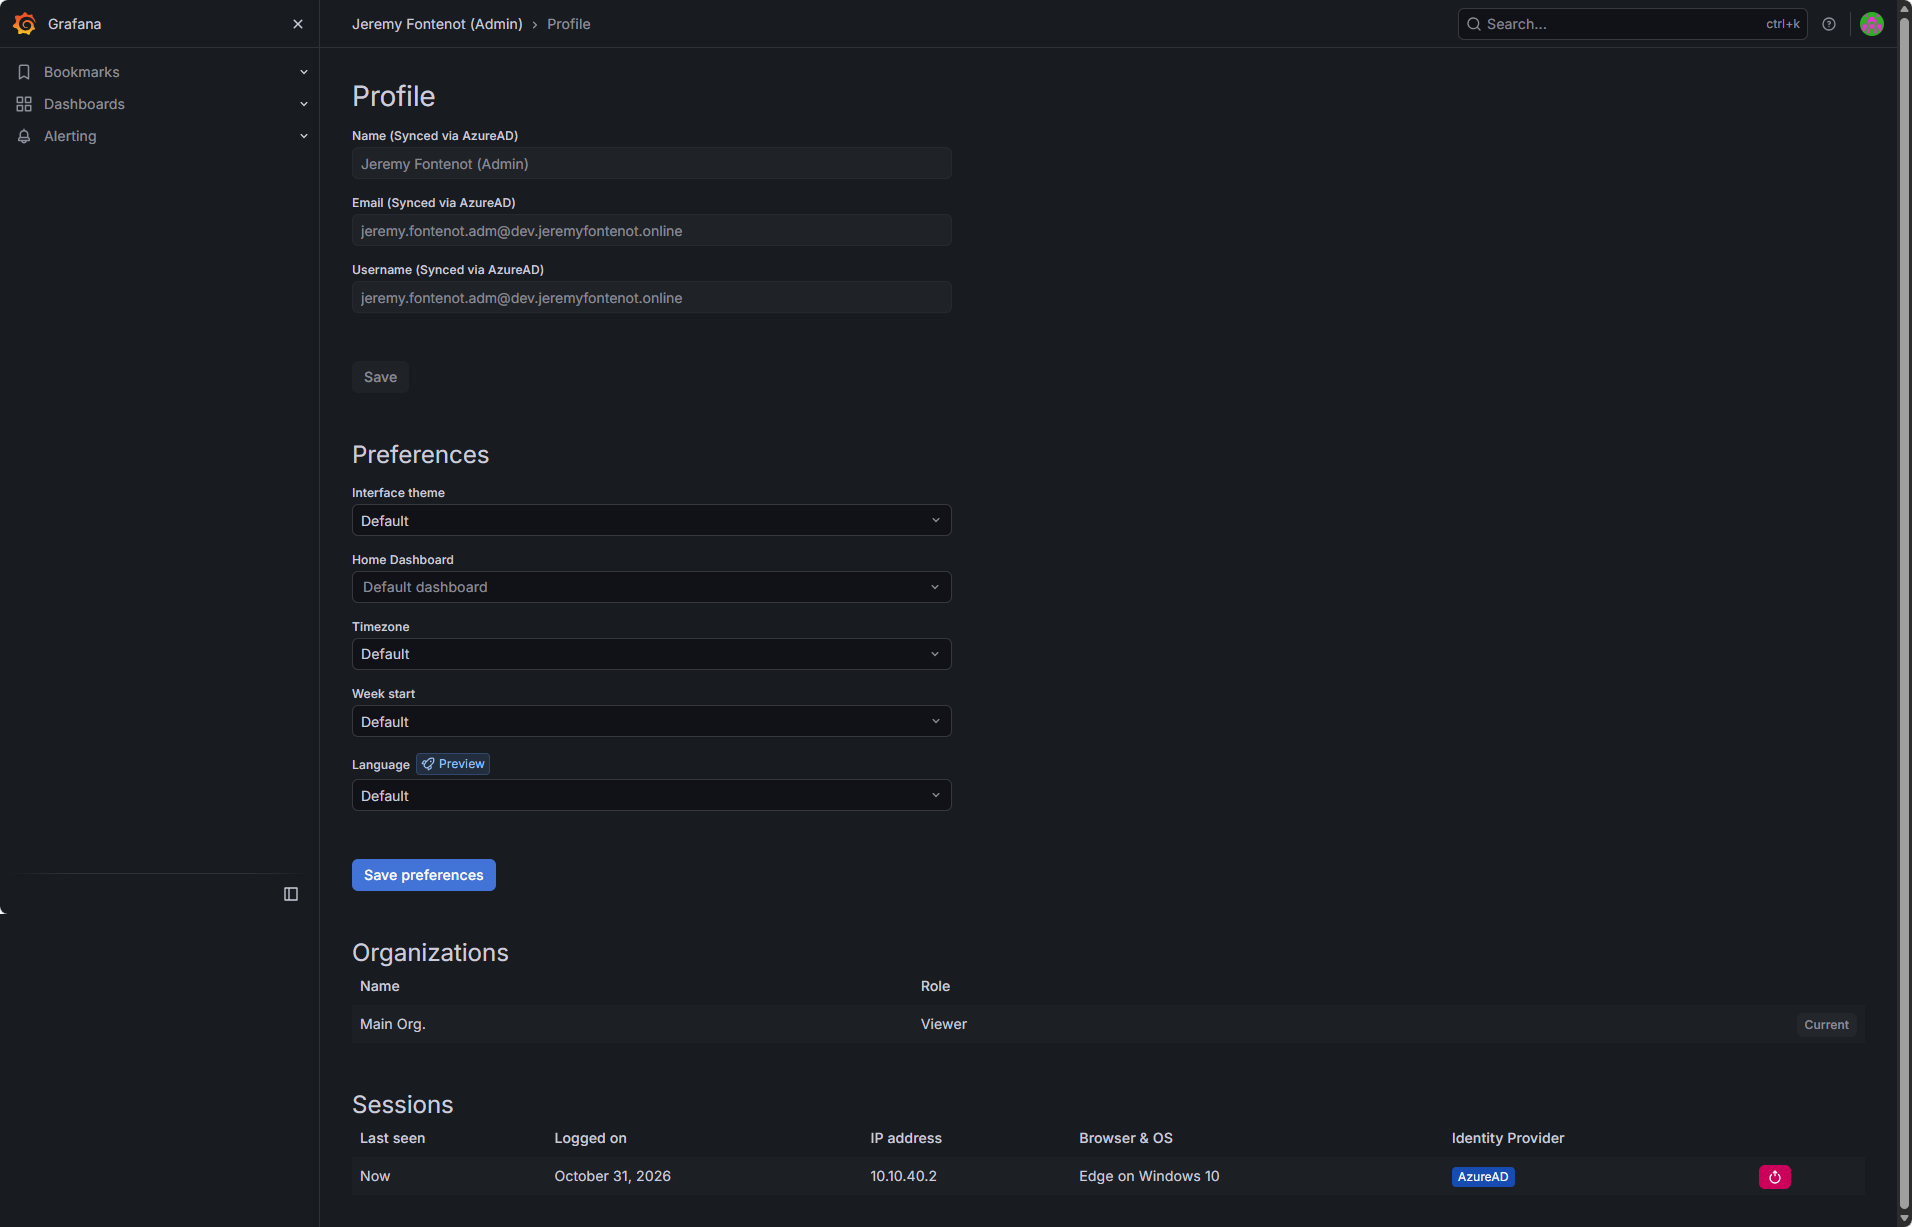
A private Ubuntu-hosted Grafana application uses trusted HTTPS, Entra OAuth, assigned-user access, and a My Apps launch tile.
Inspect AzureAD identity and Viewer proof →15 / PowerShell & automation
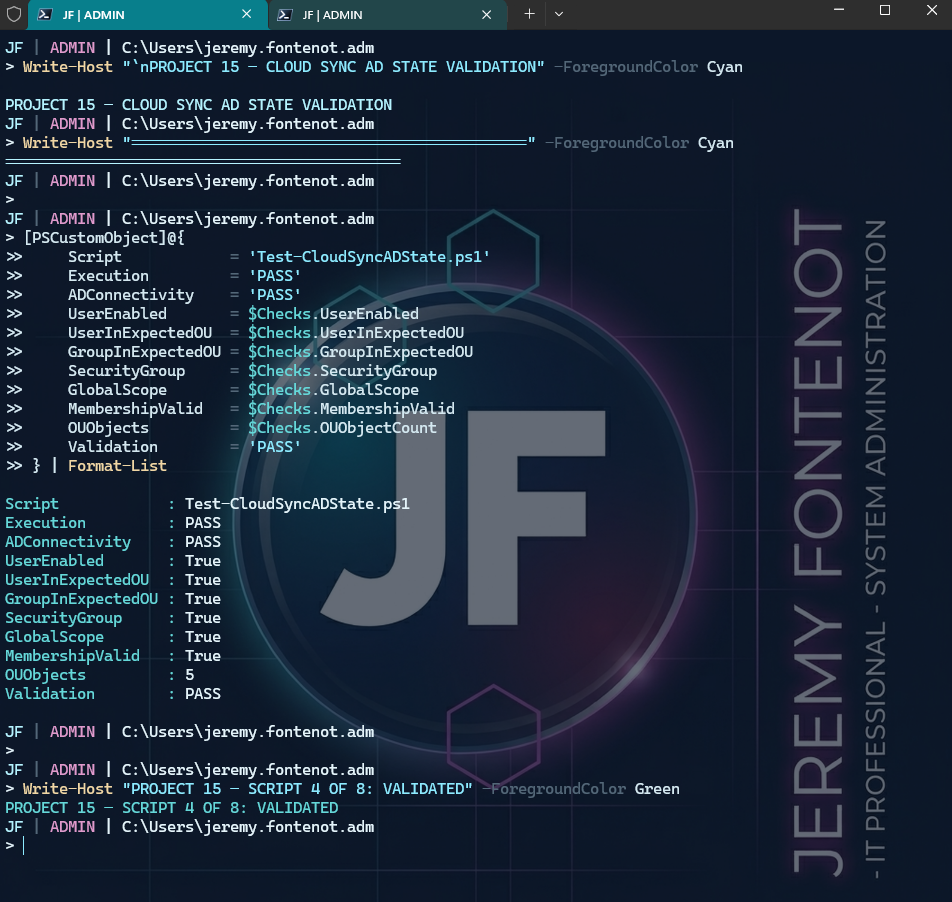
A PowerShell 7 dashboard demonstrates Microsoft Graph inventory, hybrid identity checks, Windows LAPS validation, Azure Arc inspection and guarded AD provisioning.
Inspect original PASS evidence →A practical approach
My portfolio follows the path from skill to task, outcome, and supporting evidence. Each case study explains what the retained artifacts show and where the evidence stops.
My supplied resume describes enterprise service desk support, incident ownership, escalation, and earlier startup infrastructure work. Personal-lab projects provide a separate place to inspect technical implementation.
Read professional experience →Employment details are owner-provided in the original resume.
Completed technical work remains useful proof regardless of subsequent lab or subscription availability. Sanitized results, documentation, screenshots, and simulated scenarios are identified according to their actual scope.