Jeremy Fontenot / Technical portfolio
Skills, connected
to original proof.
Fifteen case studies. Direct technical evidence. Explore the configuration, the result, and the skill behind it.
PROJECT 15 / POWERSHELL AUTOMATION
JF Automation & Scripting Dashboard
Local PowerShell 7 workflows for cloud inventory, hybrid identity checks, Windows LAPS validation and guarded AD provisioning.
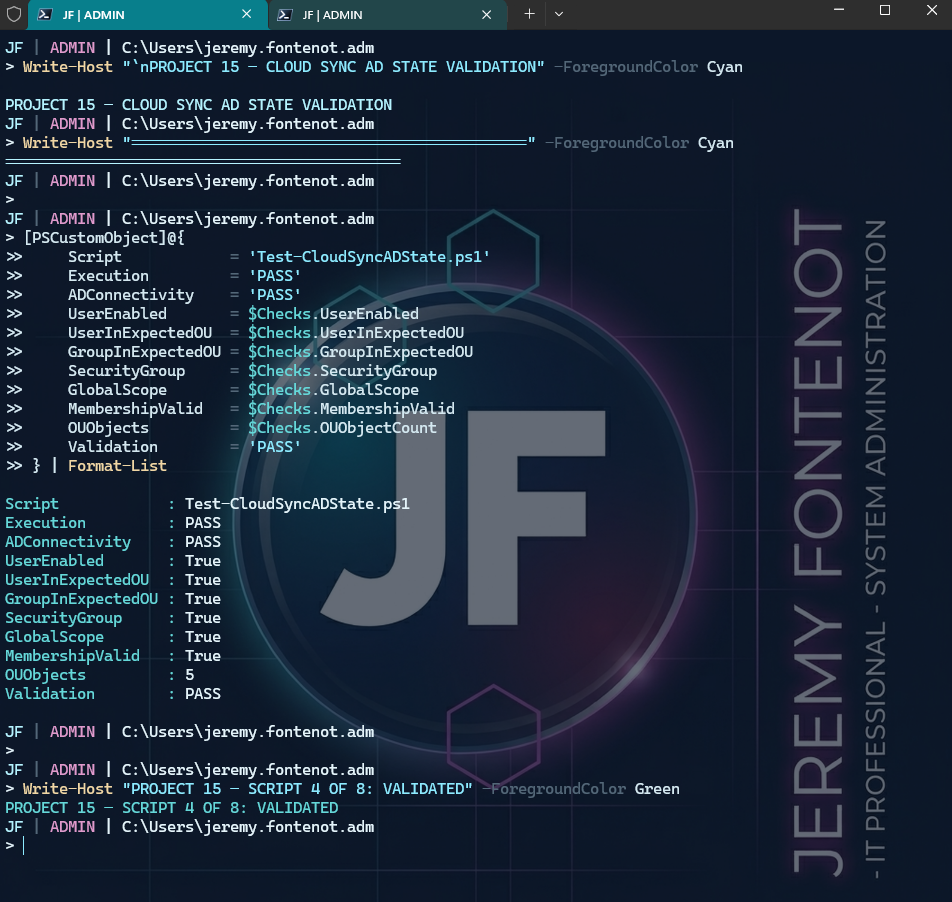
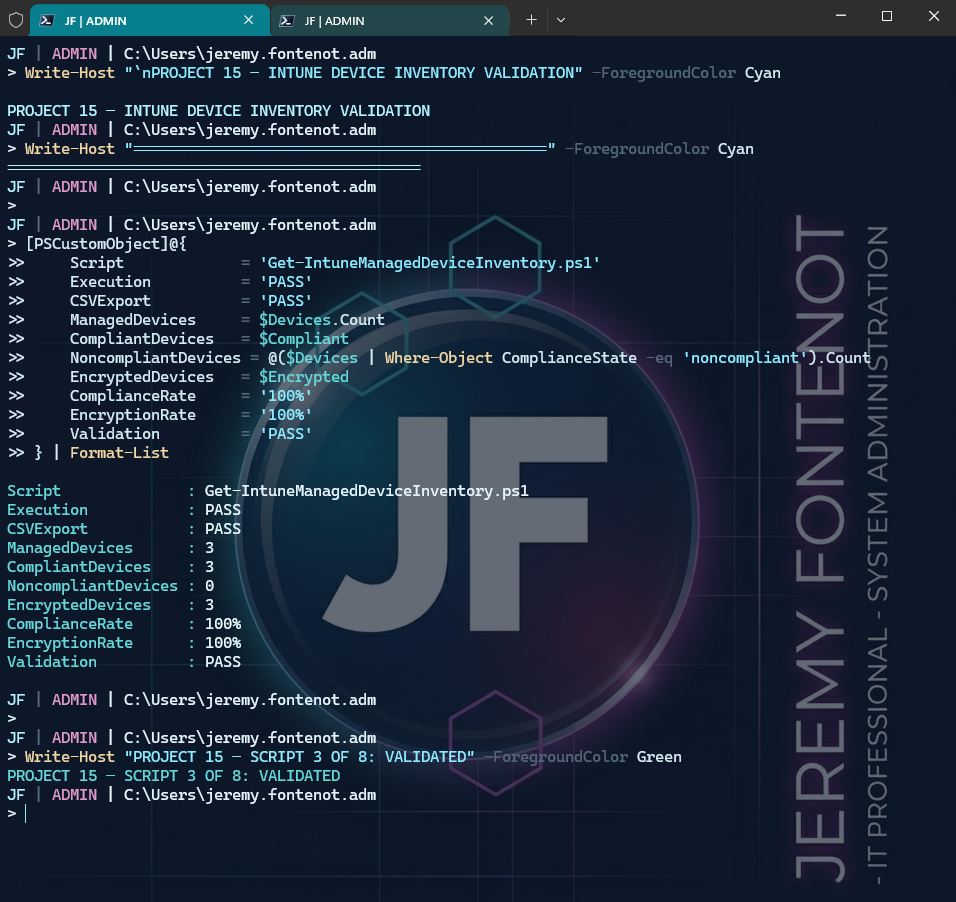
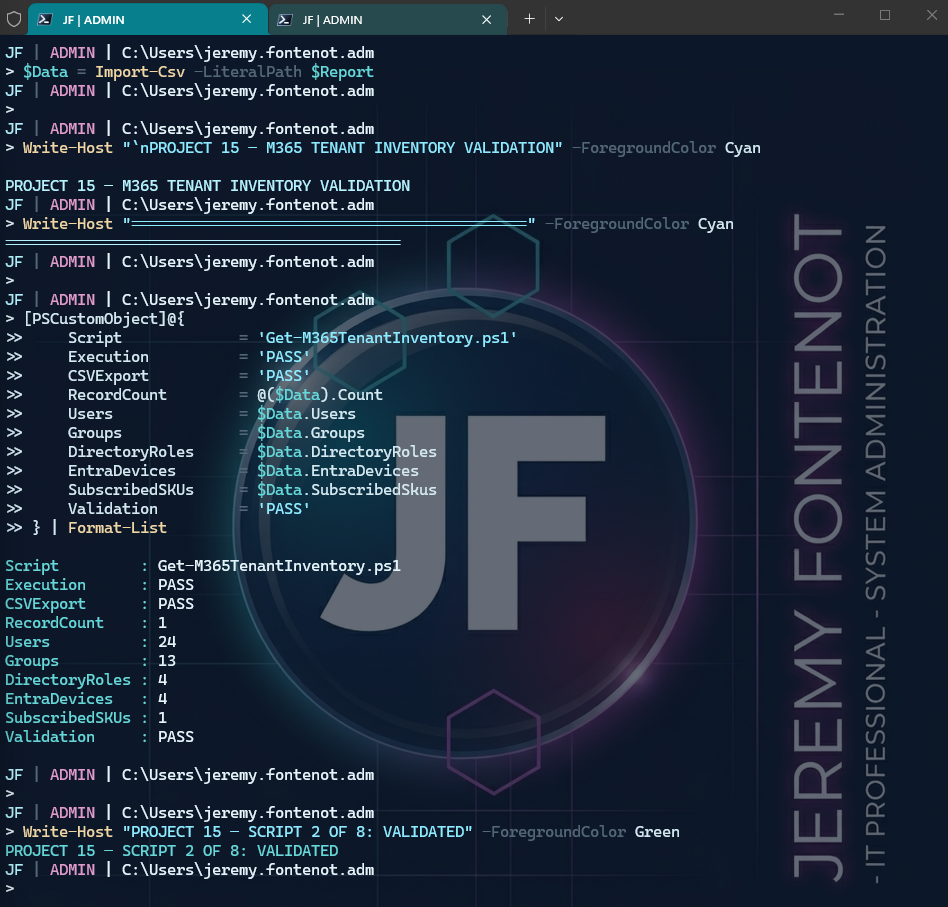
- Cloud Sync / AD state — original PASS screenshot ↗
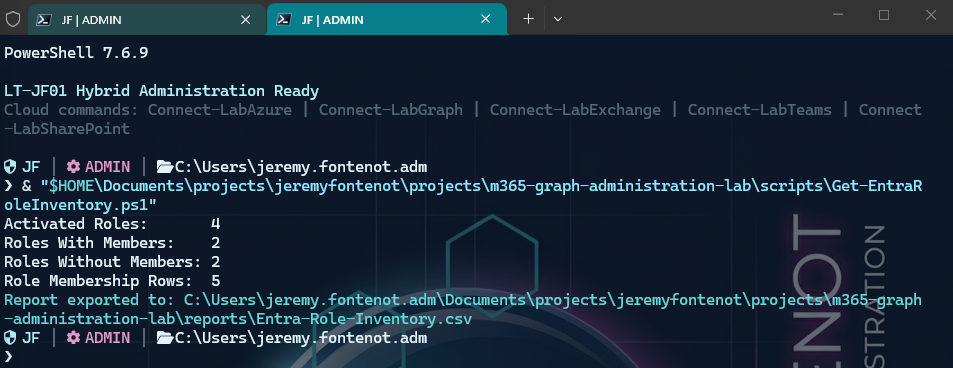
- Entra role inventory — original PASS screenshot ↗
- Intune managed devices — original PASS screenshot ↗
- Microsoft 365 tenant inventory — original PASS screenshot ↗
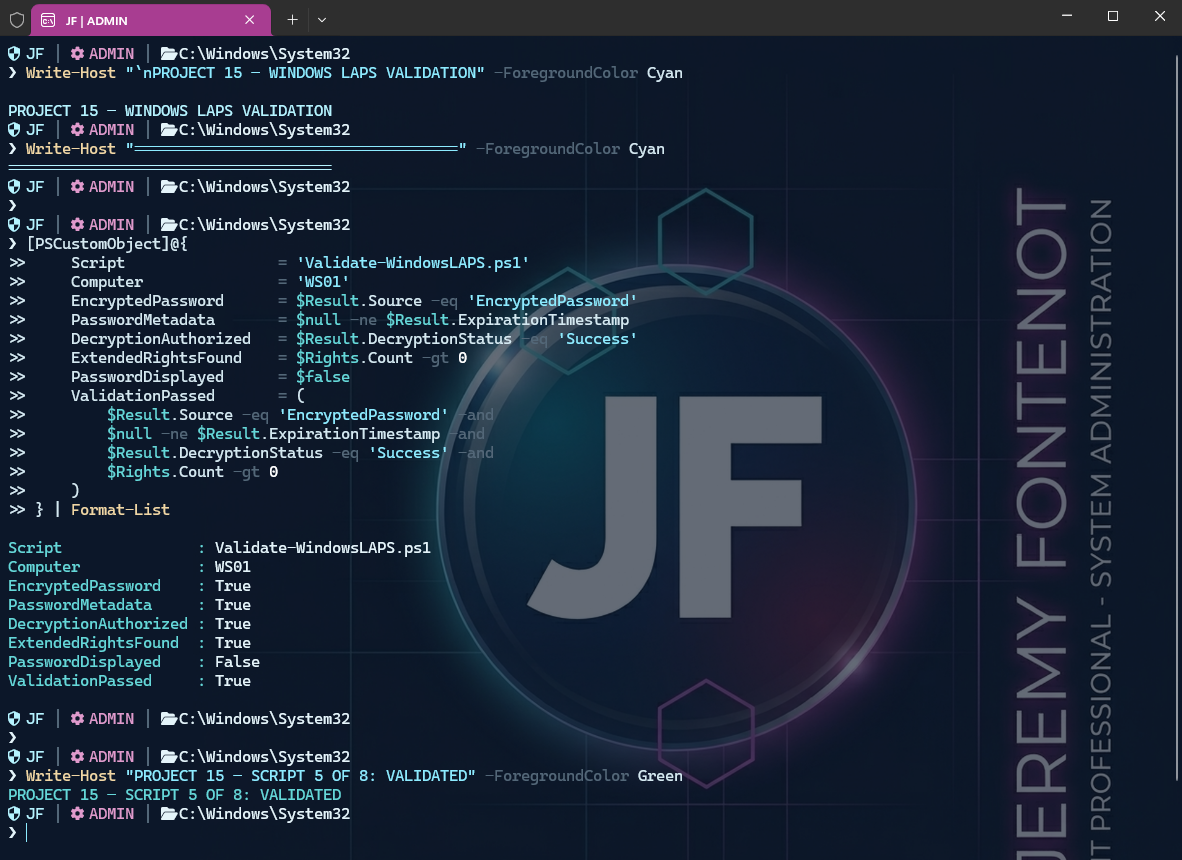
- Windows LAPS validation — original PASS screenshot ↗
Windows LAPS & Advanced Group Policy
Retained schema validation records the modern msLAPS attributes required for AD-backed Windows LAPS. Open supporting artifact
The tested unauthorized standard-user retrieval path returned no LAPS record. Open supporting artifact
Retained events record administrator-initiated rotation, local password update, AD update, and successful policy processing. Open supporting artifact
Sanitized retrieval evidence records a successful authorized LAPS retrieval. Open supporting artifact
Microsoft Entra Hybrid Identity & Cloud Sync
The retained validation record documents scoped user provisioning, Department synchronization, and source-anchor correlation. Open supporting artifact
The retained test record reports a successful Entra sign-in after an on-premises password change. Open supporting artifact
The retained test record documents security-group provisioning and one synchronized direct member. Open supporting artifact
On-Premises Microsoft Home Lab
The retained DC01 inventory derivative records Windows Server with AD DS, DNS, DHCP, and Group Policy Management roles. Open supporting artifact
Retained evidence documents one network-isolated Linux01 restore drill, guest boot and agent response, followed by cleanup. Open supporting artifact
Windows Admin Center Lab Management
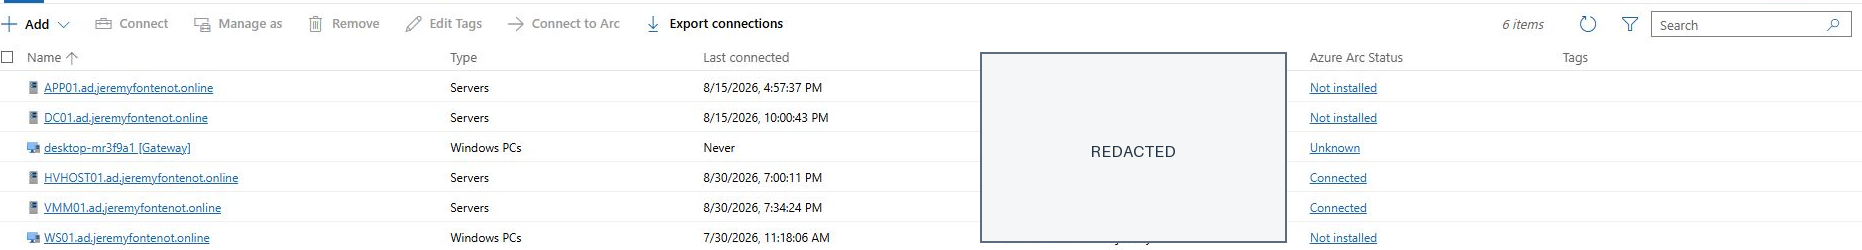
The retained Windows Admin Center screenshot shows six lab connections, including two with Connected Azure status. Open supporting artifact
SCVMM 2022 Hyper-V Management
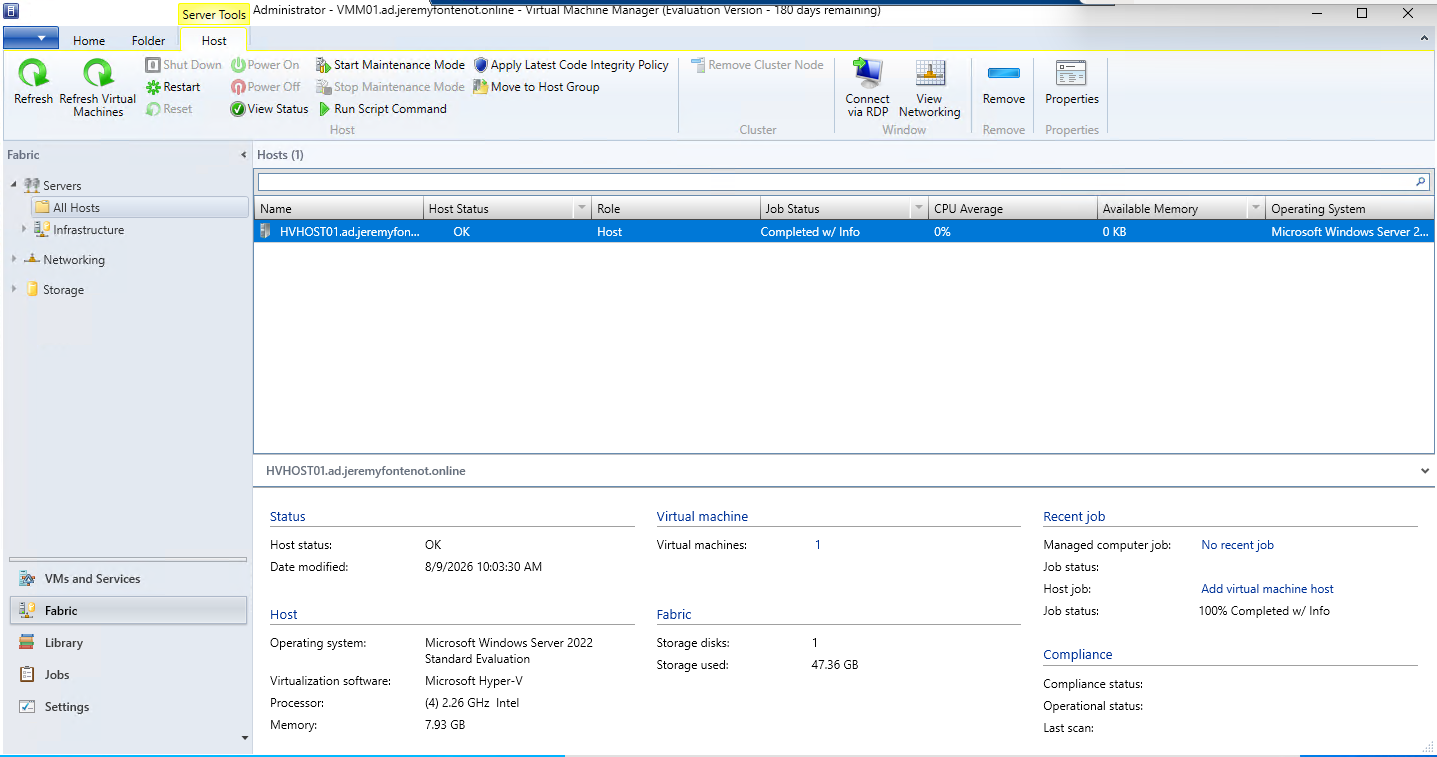
The retained VMM console capture shows HVHOST01 managed with host status OK and one virtual machine. Open supporting artifact
Azure Arc Hybrid Windows Management
The public-safe Arc summary records two connected Windows Server lab machines and running Arc services on HVHOST01. Open supporting artifact
The retained Arc summary records a SQL Server 2022 Developer instance with a succeeded SQL extension and OK telemetry uploads. Open supporting artifact
APP01 Hyper-V Storage Expansion
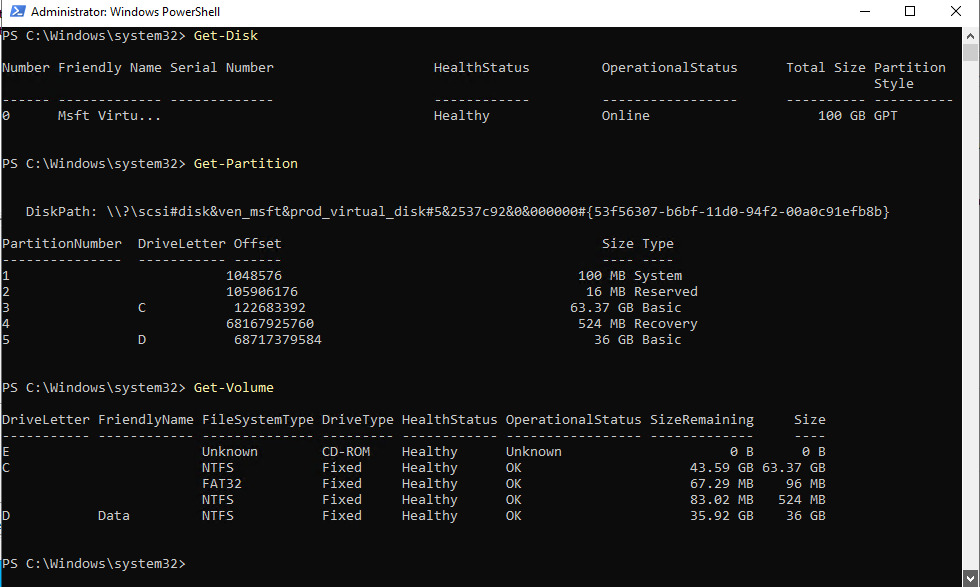
The retained guest PowerShell capture shows a healthy online 100 GB GPT disk, C: at 63.37 GB, and a 36 GB Data volume. Open supporting artifact
Cross-Platform Administration & Support Method
Retained Linux01 evidence documents an SSSD responder/socket conflict correction and successful post-remediation AD identity lookup and SSH. Open supporting artifact
Retained WS01 inventory records Windows domain membership and a true secure-channel result. Open supporting artifact
ServiceNow Request Fulfillment & Procurement Workflow
The project record documents REQ/RITM approval, Procurement and Field Services tasks, and automatic request closure in a ServiceNow PDI. Open supporting artifact
The project record documents an itil role qualifier as the cause of an assignee-selection issue, with the qualifier preserved. Open supporting artifact
Microsoft 365 Messaging & Security Administration
Sanitized command evidence records a SharedMailbox with FullAccess and SendAs delegation. Open supporting artifact
Sanitized command evidence records an enabled, enforced external-sender subject-prefix pilot rule. Open supporting artifact
The retained validation record documents Conditional Access scope remediation and a successful post-remediation MFA sign-in. Open supporting artifact
Windows Autopilot & Intune MDM Provisioning
Sanitized post-Autopilot output records Entra join, successful device authentication, and an Azure AD PRT. Open supporting artifact
Retained BitLocker validation records the captured encryption and protection state; this is personal-device lab evidence. Open supporting artifact
macOS ABM to Intune Enterprise Runbook
The retained matrix distinguishes APNs and macOS policy configuration from unperformed ABM/ADE enrollment and managed-Mac operations. Open supporting artifact
The simulated deployment scenario is a runbook, rather than proof of completed managed-Mac enrollment. Open supporting artifact
Microsoft 365 Graph Administration Lab
The supplied Get-EntraRoleInventory.ps1 implements read-only Graph reporting; retained documentation reports validation, while live CSV output is withheld. Open supporting artifact
The supplied Get-EntraStaleAccounts.ps1 implements read-only Graph reporting; retained documentation reports validation, while live CSV output is withheld. Open supporting artifact
The supplied Get-IntuneManagedDeviceInventory.ps1 implements read-only Graph reporting; retained documentation reports validation, while live CSV output is withheld. Open supporting artifact
The supplied Get-M365GroupMembership.ps1 implements read-only Graph reporting; retained documentation reports validation, while live CSV output is withheld. Open supporting artifact
The supplied Get-M365LicenseAssignment.ps1 implements read-only Graph reporting; retained documentation reports validation, while live CSV output is withheld. Open supporting artifact
The supplied Get-M365TenantInventory.ps1 implements read-only Graph reporting; retained documentation reports validation, while live CSV output is withheld. Open supporting artifact
The supplied Get-M365UserInventory.ps1 implements read-only Graph reporting; retained documentation reports validation, while live CSV output is withheld. Open supporting artifact
Retained troubleshooting notes document correcting directory-role membership query parameters and adding a missing sign-in activity scope. Open supporting artifact
PROJECT 14 / IDENTITY & SECURE APPLICATIONS
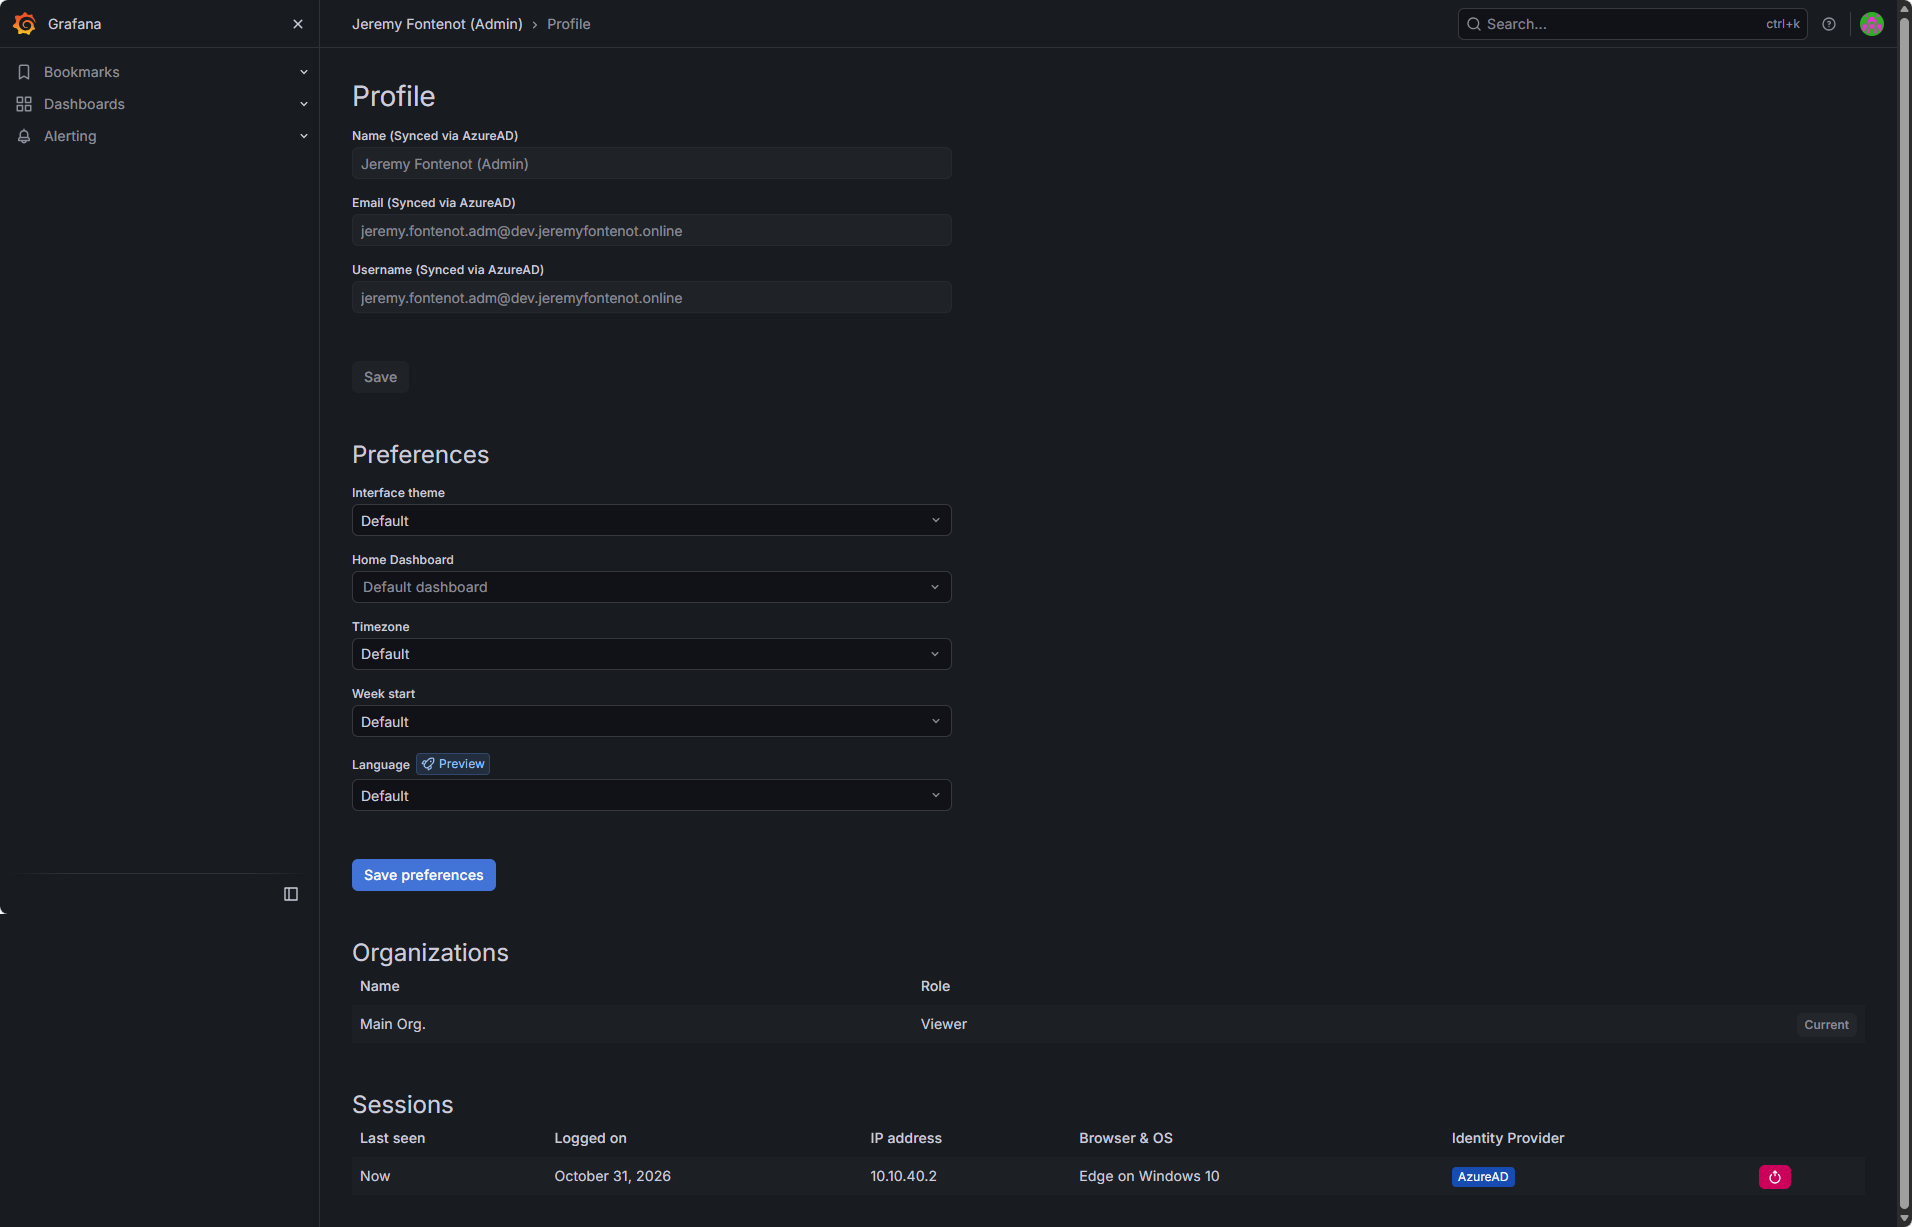
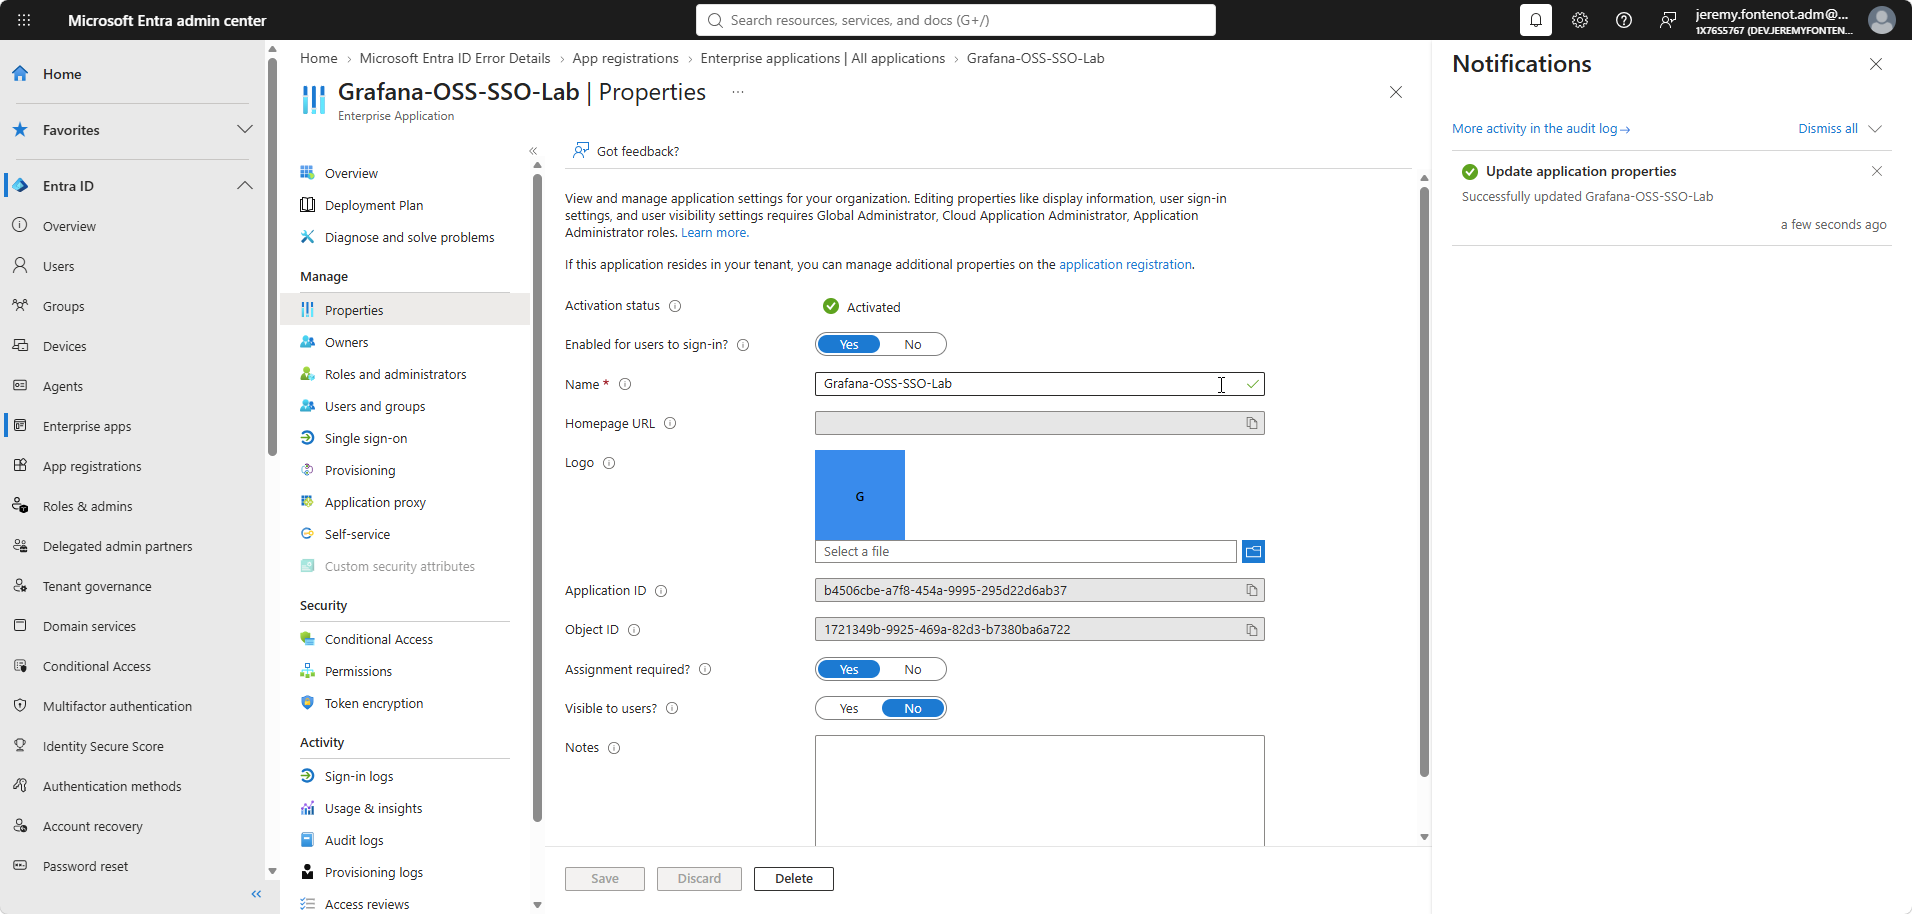
Grafana OSS + Microsoft Entra SSO
Grafana’s profile shows AzureAD-synchronized identity, Viewer authorization, and the session identity provider. Open identity and Viewer proof
Entra enterprise application properties show Assignment required enabled. Open application assignment proof
Original screenshots show the running Linux service, certificate issuance, HTTPS access, and My Apps integration. Explore all 19 original screenshots