PROJECT 01 / IDENTITY & ACCESS
Windows LAPS & Advanced Group Policy
Retained schema validation records the modern msLAPS attributes required for AD-backed Windows LAPS.
Jeremy Fontenot / Technical portfolio
Browse 15 case studies by technical area. Each project links to its implementation narrative and a direct supporting artifact.
Browse by capability
15 projects shown
PROJECT 01 / IDENTITY & ACCESS
Retained schema validation records the modern msLAPS attributes required for AD-backed Windows LAPS.
PROJECT 02 / IDENTITY & ACCESS
The retained validation record documents scoped user provisioning, Department synchronization, and source-anchor correlation.
PROJECT 03 / WINDOWS INFRASTRUCTURE
The retained DC01 inventory derivative records Windows Server with AD DS, DNS, DHCP, and Group Policy Management roles.
PROJECT 04 / WINDOWS INFRASTRUCTURE
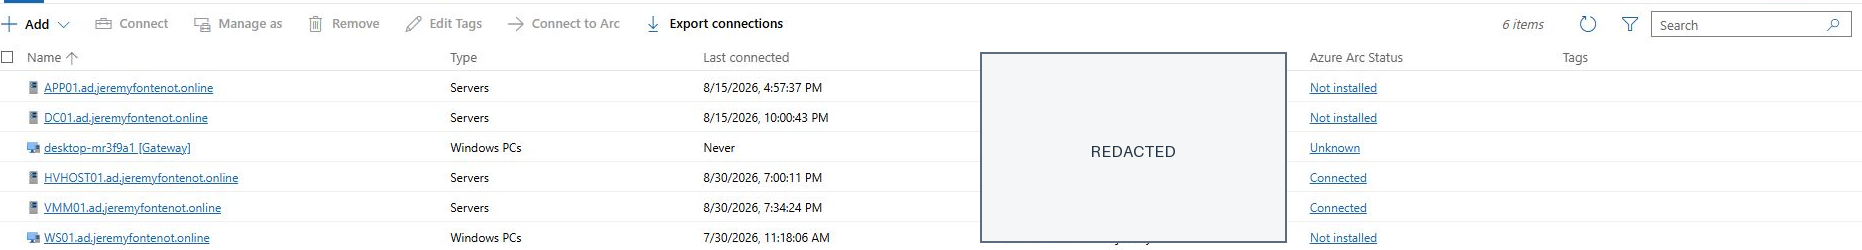
The retained Windows Admin Center screenshot shows six lab connections, including two with Connected Azure status.
PROJECT 05 / VIRTUALIZATION
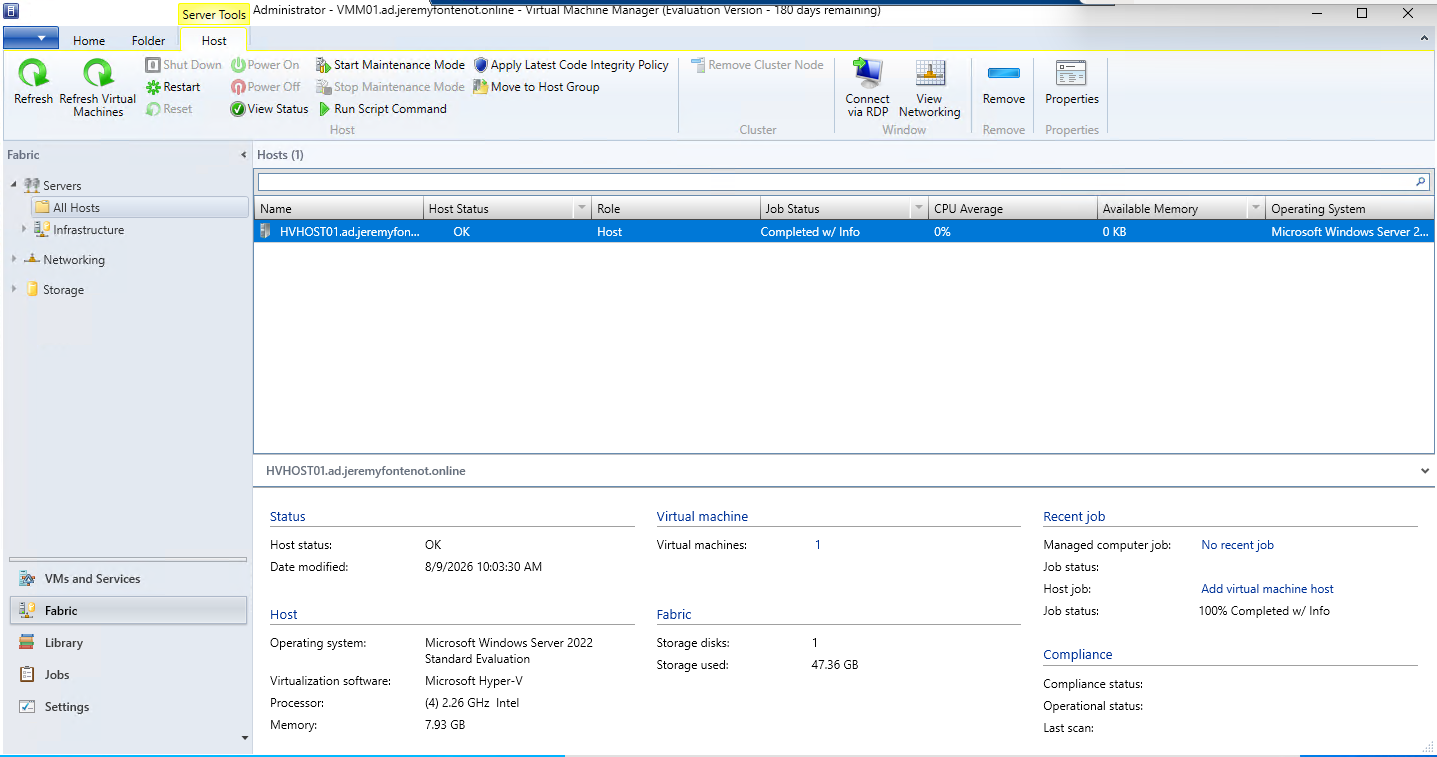
The retained VMM console capture shows HVHOST01 managed with host status OK and one virtual machine.
PROJECT 06 / CLOUD & M365
The public-safe Arc summary records two connected Windows Server lab machines and running Arc services on HVHOST01.
PROJECT 07 / VIRTUALIZATION
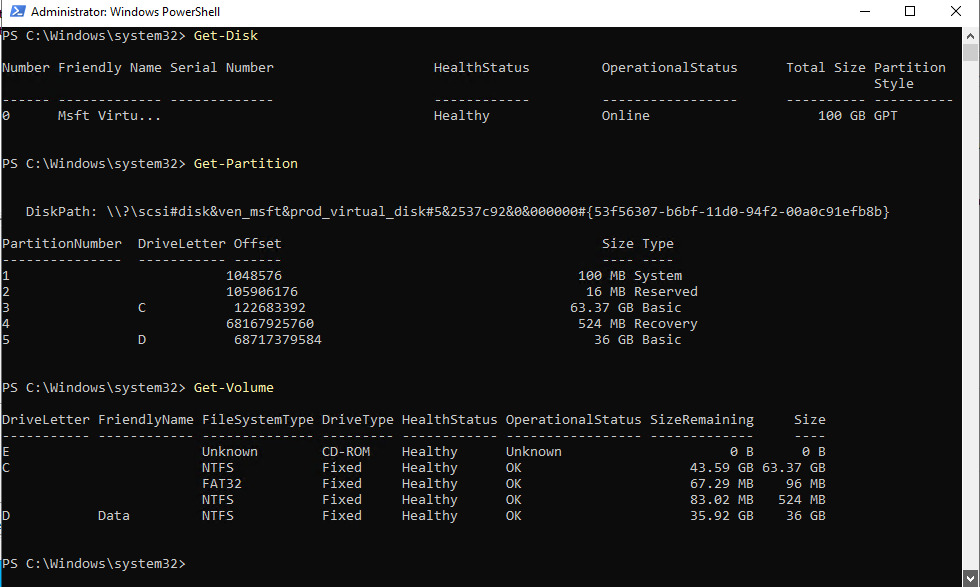
The retained guest PowerShell capture shows a healthy online 100 GB GPT disk, C: at 63.37 GB, and a 36 GB Data volume.
PROJECT 08 / WINDOWS INFRASTRUCTURE
Retained Linux01 evidence documents an SSSD responder/socket conflict correction and successful post-remediation AD identity lookup and SSH.
PROJECT 09 / ITSM
The project record documents REQ/RITM approval, Procurement and Field Services tasks, and automatic request closure in a ServiceNow PDI.
PROJECT 10 / CLOUD & M365
Sanitized command evidence records a SharedMailbox with FullAccess and SendAs delegation.
PROJECT 11 / ENDPOINT MANAGEMENT
Sanitized post-Autopilot output records Entra join, successful device authentication, and an Azure AD PRT.
PROJECT 12 / ENDPOINT MANAGEMENT
The retained matrix distinguishes APNs and macOS policy configuration from unperformed ABM/ADE enrollment and managed-Mac operations.
PROJECT 13 / AUTOMATION
Seven retained Microsoft 365 reporting scripts plus a new delegated Graph JSON export application. Eight Pester tests passed locally; source and tests are published while tenant reports remain private.
PROJECT 14 / IDENTITY & ACCESS
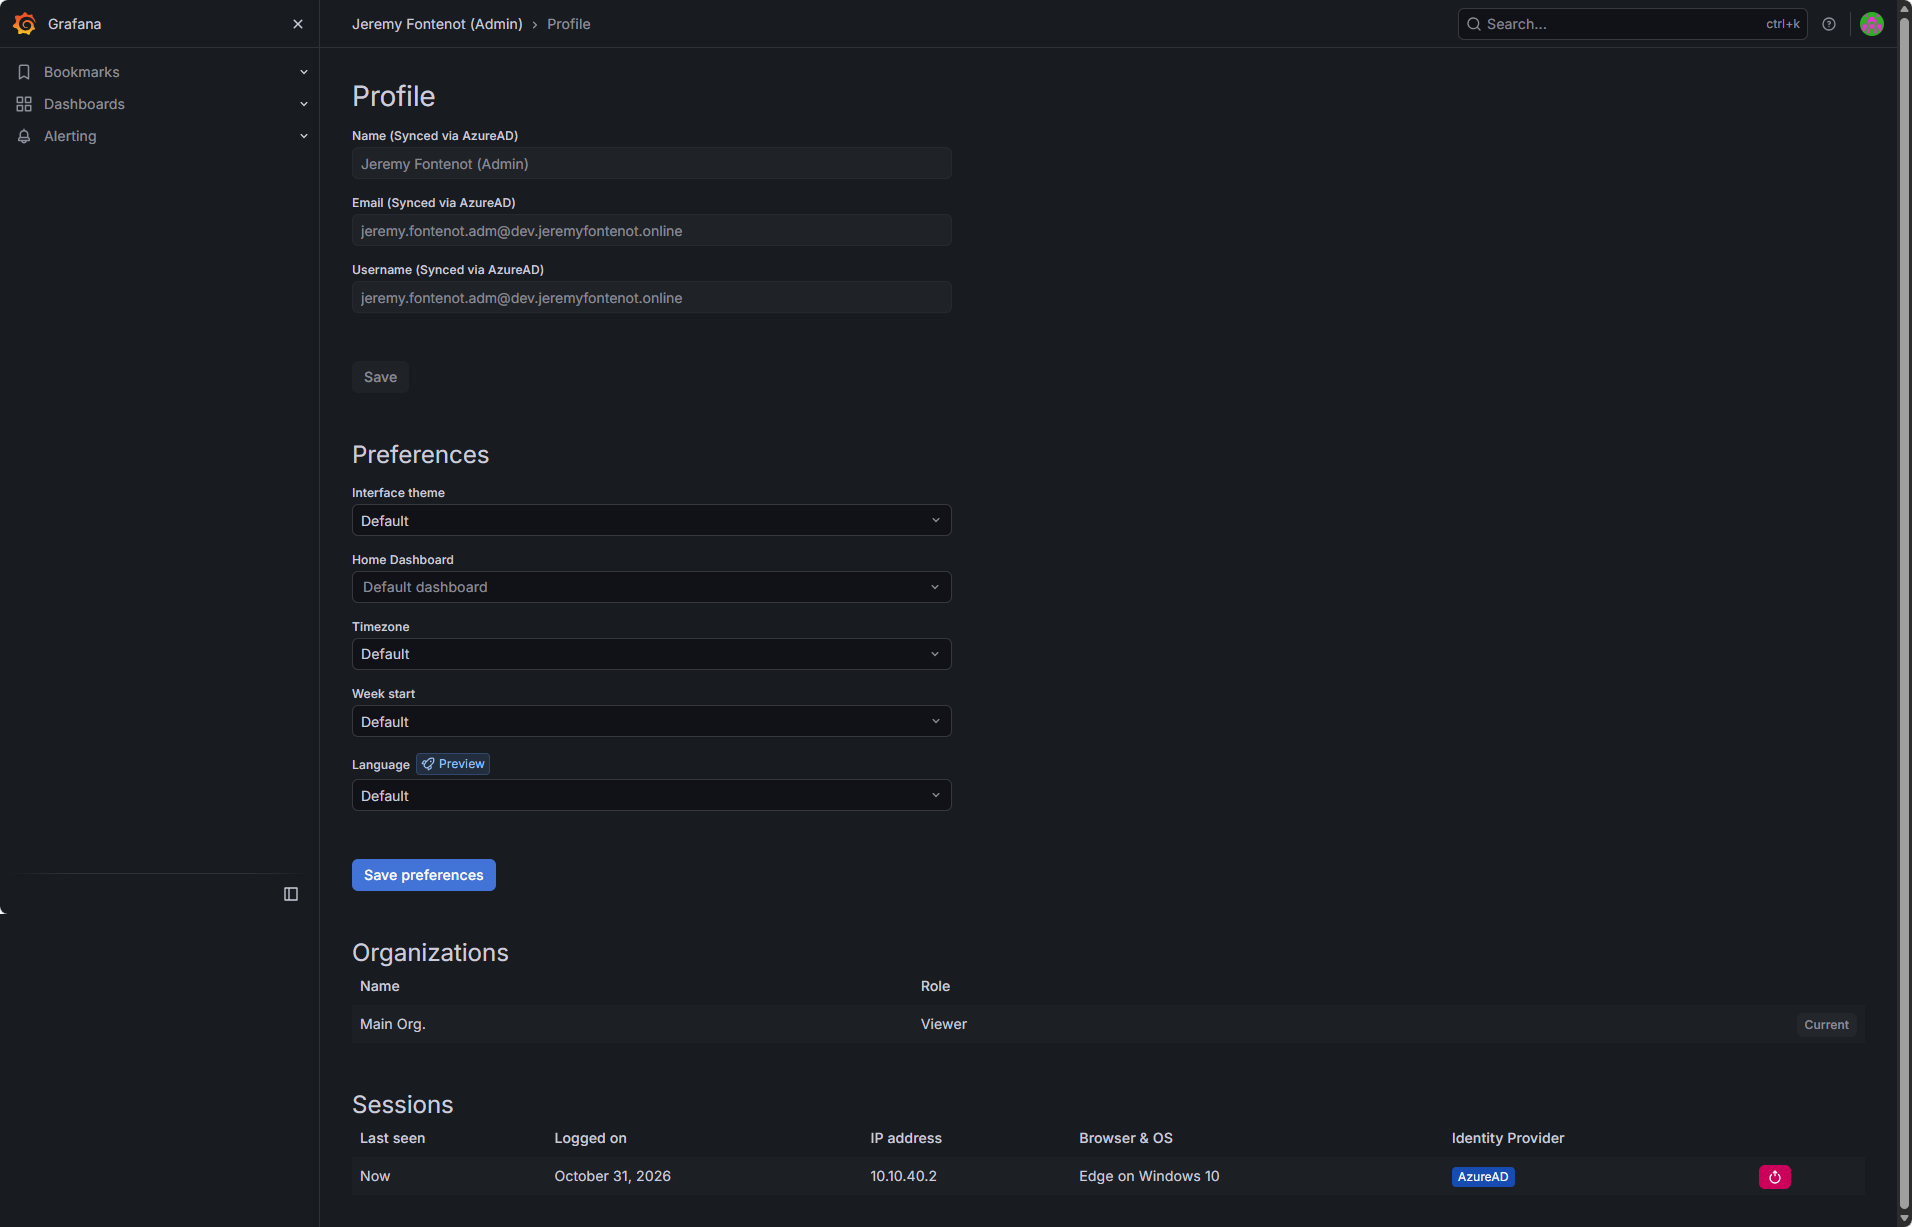
Implemented Ubuntu-hosted Grafana with trusted HTTPS, Microsoft Entra OAuth sign-in, Viewer authorization, assigned-user access, and a My Apps launch tile. The retained lab record documents successful certificate-renewal and deployment-hook simulation.
PROJECT 15 / AUTOMATION
PowerShell 7 dashboard with eight administration cards, seven validated workflows, execution logs, Graph inventory, LAPS checks, and guarded AD provisioning.
Technical focus